From the archive: this article was published in August 2016 and is kept for reference. Tools, versions and figures may have changed since.
On this page 15
Insurance and customer relationship management share a problem: many parties need to agree on facts about a customer, a policy or a product, and each keeps its own copy. Insurers, brokers, reinsurers, repair shops, hospitals and retailers all hold records that disagree, and reconciling them costs time and invites fraud.
A blockchain can help when several organizations need a shared, tamper-evident record that none of them controls alone. It does not help when one company owns the whole process. This post covers the use cases where it has a real case, how to handle documents and personal data, and the lessons from projects that did not work out.
When blockchain fits
Use these questions as a filter before any pilot:
- Do several independent parties write to the same record? If only one company does, a database with audit logging is simpler.
- Is disagreement or fraud between them a real cost? The ledger’s value is that nobody can quietly rewrite history.
- Can the parties agree on governance? Someone has to decide who runs nodes, who may join and how rules change.
Most insurance and customer-data use cases that pass this filter run on permissioned networks with known members, not public chains.
Insurance use cases
Claims and proof of facts
Many claims hinge on facts that are hard to verify: when a policy was bought, whether an item existed and who owned it, whether a document is genuine. A ledger can record:
- the date and time a policy was issued or a product was bought
- ownership and location changes of an insured asset
- fingerprints (hashes) of documents such as medical reports, repair invoices and police reports, so any later alteration is detectable
With these records shared between insurer, broker and service providers, routine claims need fewer manual checks.
Fraud detection across insurers
Duplicate claims for the same loss with several insurers are a long-standing fraud pattern. A shared registry of claim fingerprints lets insurers spot duplicates without exposing the claim details to competitors. The privacy design matters: store hashed or tokenized identifiers, not names, and agree up front on what each member can see.
Reinsurance and multi-party contracts
Reinsurance involves several parties exchanging premiums, exposure data and claims under complex treaties. A shared ledger can keep one version of contract terms and settlement data, cutting reconciliation work.
This is also where the most instructive failure happened. B3i, an industry consortium of large insurers and reinsurers set up in 2016 to build exactly this, entered insolvency in 2022 after failing to secure further funding. The technology worked in pilots; the business case and shared funding did not hold together. Any consortium project should plan governance and cost-sharing as carefully as the software.
Parametric insurance
Parametric policies pay a fixed amount when a measurable event occurs, such as a flight delay over a set time or rainfall below a threshold, instead of assessing actual losses. A smart contract can hold the terms and pay out automatically when a trusted data feed (an oracle) reports the event.
AXA’s Fizzy, a flight-delay product on Ethereum, ran from 2017 and was discontinued in 2019. Projects such as Etherisc have continued the approach. The hard parts are the oracle (who supplies the data and why trust it) and regulation (payouts still need a licensed insurer), not the contract itself.
Customer data use cases
The same ideas apply in customer relationship management (CRM), where the record is about a customer rather than a policy.
Product provenance and warranties
A product registered on a shared ledger at sale, with its serial number and purchase date, makes warranty claims simpler: the manufacturer, retailer and service center all see the same record. For premium goods, the same record supports authenticity checks and resale history, which builds customer trust.
Consent records
Customers grant and withdraw consent for marketing, data sharing and processing. A ledger can keep a tamper-evident log of consent events shared between a company and its partners, so every party can prove what the customer agreed to and when.
Verifiable customer credentials
Instead of each company collecting and storing the same identity documents, a customer can hold credentials issued by a trusted party (a bank confirming KYC, an insurer confirming cover) and present them when needed. The W3C Verifiable Credentials standard defines how such credentials are issued and checked. The ledger, when one is used, typically holds only issuer keys and revocation lists, not the credentials themselves.
Loyalty programs
Points that work across partner brands are a reconciliation headache, since each partner keeps its own balance. Tokenized loyalty points on a shared ledger give every partner the same balance and transaction history. This is one of the lower-risk pilots, because it sits beside the core CRM rather than replacing it.
Keeping documents and personal data off-chain
There are two ways to put a document on a blockchain:
- Store the file itself on-chain. This is technically possible but costly, and every node holds a permanent copy. For personal data it is usually the wrong choice.
- Store the file elsewhere and record only its hash on-chain. This is the standard approach.
A cryptographic hash function such as SHA-256 turns any input into a fixed-length fingerprint. The same input always gives the same output on any computer, and any change to the input gives a completely different one. Hashing the word blockchain with SHA-256, for example, always gives:
ef7797e13d3a75526946a3bcf00daec9fc9c9c4d51ddc7cc5df888f74dd434d1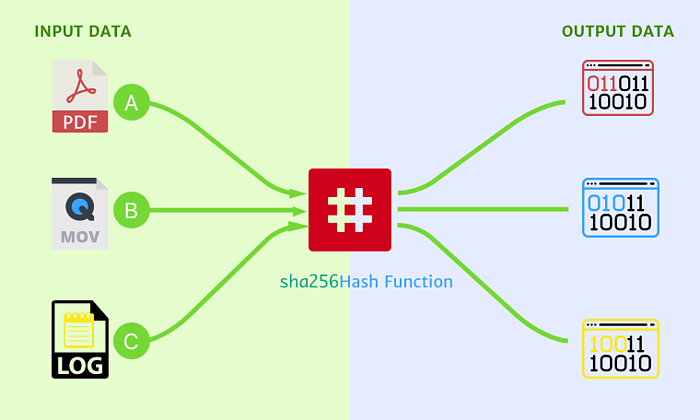
To verify a document later, hash it again and compare the result with the value on the ledger. If they match, the document has not changed since it was recorded, and the block’s timestamp shows when it was recorded.
Privacy law and immutability
Data protection laws such as the GDPR give people rights to correct and erase their data, which conflicts with a ledger nobody can change. The usual design:
- Keep personal data in a conventional, access-controlled store.
- Put only hashes, references or consent events on-chain, and avoid hashing small, guessable values (such as a phone number) on their own, since they can be recovered by brute force. Add a random salt or use keyed hashes.
- Delete the off-chain data and its keys when a customer asks for erasure, leaving an on-chain reference that no longer points to anything personal.
Get a legal review of this design for your jurisdictions; it is a common point of scrutiny.
What blockchain does not solve
- Bad input data. A ledger proves a record has not changed since it was written, not that it was true when written.
- Integration. Policy admin systems, claims platforms and CRMs still need to connect to the ledger, which is usually most of the work.
- Regulation. Licensing, capital rules and consumer protection still apply in full.
Where to start
Pick one narrow process with several parties and a clear cost of disagreement: a duplicate-claims registry, warranty verification, or a shared consent log. Run it beside existing systems, measure the reconciliation work it removes, and expand only if it pays off.
For related reading, see blockchain, stablecoins and smart contracts for a broader business view, or blockchain innovation patterns. Lightrains offers blockchain development services, including smart contract design, tokenization and integration with existing insurance and CRM systems.
This article originally appeared on lightrains.com
Leave a comment
To make a comment, please send an e-mail using the button below. Your e-mail address won't be shared and will be deleted from our records after the comment is published. If you don't want your real name to be credited alongside your comment, please specify the name you would like to use. If you would like your name to link to a specific URL, please share that as well. Thank you.
Comment via email